Scienceware
-
In-page Prompt Injections against LLM Web Agents 2026
Scienceware we used for the data collection and analysis.
-
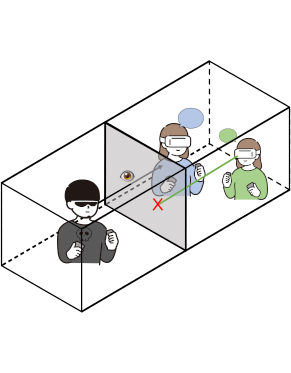
Omniscience attacks 2026
These attacks showcase how users creating worlds in metaverse platforms could create covert user surveillance and manipulation without software vulnerabilities or developer-level privileges.
-
CHARON 2025
CHARON is a polyglot static analysis engine for detecting vulnerabilities in scripting languages' native extensions.
-
YuraScanner 2025
One of the first task-driven, autonomous LLM-powered web application scanners.
-
SURFER 2024
A static analysis tool to find SSRF candidates in PHP CPGs.
-
Arachnarium 2024
Arachnarium is a plug-and-play benchmark framework for crawlers that can run experiments at scale against both local, standalone web applications and live websites.
-
JAW (Javascript Analysis frameWork) 2021
JAW is a scalable framework to analyze client-side JavaScript programs. JAW can be used to conduct interactive and exploratory analysis of JavaScript code.
-
Black Widow 2020
Black Widow is a new data-driven web application scanner that combines three techniques: navigation modeling, graph traversing, and tracking inter-state dependencies.
-
Ad-Versarial 2019
We released scripts, datasets, and trained YOLOv3 models of our work Ad-versarial: Defeating Perceptual Ad-Blocking.
-
Fidelius 2019
Fidelius is a new architecture with a trusted path for user I/O and web enclaves to protect user secrets even if the entire underlying browser and OS are fully controlled by a malicious attacker.
-
Deemon 2017
Deemon detects CSRF in PHP/SQL web applications by combining dynamic analysis with property graphs.
-
Guenther 2015
Guenther tests web applications against server-side request (SSR) abuse, including Web Origin Laundering, Server-Side Request Forgery (SSRF), and other abuses.
-
jÄk (yet Änother krawler, ja!) 2015
jÄk [jAEk] is a crawler that uses function hooking and other dynamic analysis techniques to identify JavaScript event function registrations to explore the attack surface of web applications.