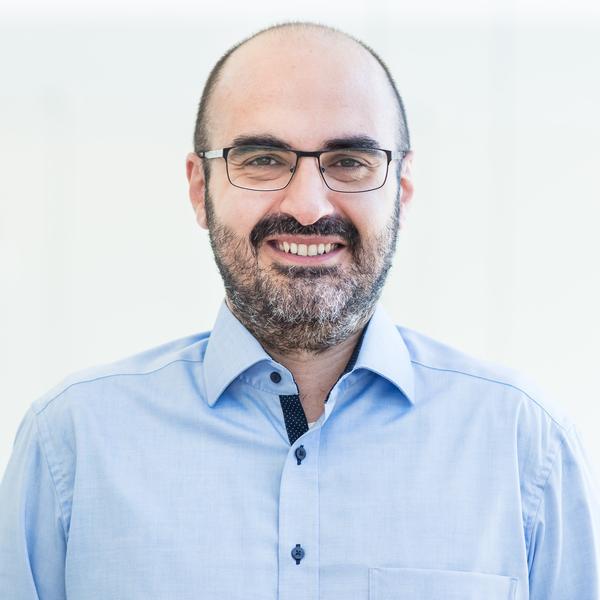
I am a faculty member at CISPA Helmholtz Center for Information Security, leading the Application Security (AppSec) research group. These are our broad areas of interest:
- Web security and web application security
- Security of emerging technology (e.g., metaverse/WebXR, etc.)
- Program analysis (e.g., dynamic/static, client and server, etc.)
- ML/AI for program analysis
Research
Autonomous vulnerability detection and analysis:
- Autonomous web scanners:
- 🛠️ YuraScanner (LLM-based scanner) [NDSS '25]
- MAK (an RL-based crawler) [DSN 2025]
- Web application scanners:
- Systematization of knowledge of crawlers [Sec '24]
- 🛠️ Black Widow [IEEE SP 2021]
- 🛠️ jAEk [RAID 2015]
Vulnerability analysis at scale
- Vulnerabilities: Prompt injections [CCS 2026], DOM gadgets [CCS 2025], request forgeries and request hijacking (CSRF [🏆IEEE S&P 2024, IEEE S&P 2022, Sec '21, Sec '24, CCS 2017, RAID 2021] and SSRF [Sec '24, RAID 2016]), link previews [NDSS 2020], code-less injections/DOM clobbering [🏆IEEE S&P ‘23], open redirect [NDSS 2025], web API security [NDSS 2019], compression bombs [Sec '15], logic vulnerabilities [NDSS 2014]
- Evaluation of methods/techniques: Sampling strategies [CCS 2026], crawlers [Sec '24]
- Tools and techniques: 🛠️ JAW (JavaScript Analysis Framework), 🛠️ Arachnarium, 🛠️ CHARON (a multi-language static analysis engine)
Security of the web platform and emerging technology
- Security of immersive web platforms [ACM CCS 2024, EuroS&P 2025]
- Permission rationales [🏆CHI 2025], web enclaves and trusted user I/O path (Fidelius [IEEE SP 2019])
- Security of RAG-based systems [arXiv '24]
- Security of perceptual ad-blocking [CCS 2019] and detection of adversarial physical attacks [IEEE DLS 2020]
Cyberattacks
- Clickbait PDFs [ACSAC 2023, EuroS&P '24, IEEE SP 2026]
- Buying and selling of social media accounts [IMC 2025]
Awards
- USENIX Security '26 - Distinguished reviewer award
- IEEE EuroS&P 2025 - Best paper award: CHARON: Polyglot Code Analysis for Detecting Vulnerabilities in Scripting Languages Native Extensions
- CHI 2025 - Best paper award: Permission Rationales in the Web Ecosystem: An Exploration of Rationale Text and Design Patterns
- IEEE SP '24 - Distinguished paper award: The Great Request Robbery: An Empirical Study of Client-side Request Hijacking Vulnerabilities on the Web. Proceedings of the 45th IEEE Symposium on Security and Privacy.
- CSAW'23 Europe - 2nd place, Applied Research Competition (ARC), Grenoble INP, Esisar, Valence, France, Nov 2023: It's (DOM) Clobbering Time: Attack Techniques, Prevalence, and Defenses
- IEEE SP '23 - Two distinguished paper awards:
- It's (DOM) Clobbering Time: Attack Techniques, Prevalence, and Defenses. Proceedings of the 44th IEEE Symposium on Security and Privacy.
- The Leaky Web: Automated Discovery of Cross-Site Information Leaks in Browsers and the Web. Proceedings of the 44th IEEE Symposium on Security and Privacy.
Service
Chair
- PC co-chair: USENIX Security (2025)
- Vice PC chair: USENIX Security (2023, 2024)
- General co-chair for IEEE EuroS&P (2020)
- PC co-chair for SECTEST 2015
- Publicity chair for ACM CCS (2017)
- Publication chair for DIMVA (2022, 2021)
Committee
- PC member: USENIX Security (2027, 2026, 2022, 2021, 2020, 2019), IEEE S&P (2027, 2024, 2023, 2022, 2021), ACM CCS (2023, 2021, 2020, 2018), IEEE EuroS&P (2026, 2023, 2022, 2020), ACSAC (2023, 2022, 2021, 2020, 2019, 2018, 2017), ACM AsiaCCS (2027, 2022, 2021, 2020, 2019), The Web Conference WWW (2023, 2022, 2021, 2020), DIMVA (2023, 2022, 2021, 2020), RAID (2022), SecWeb (2022, 2020), MadWeb (2026), EuroSec (2022, 2021, 2020, 2019), ISC (2019), CARDS (2019), USENIX WOOT (2018), ACM CCS Poster (2016), IWCC (2016, 2015), DEPEND (2016, 2015), WTMC (2016), STAST (2014), NBiS (2014)
- Awards committee: USENIX Security (2026)
- ACM CCS Doctoral Symposium (2026, 2025, 2024)
- USENIX Security invited talks committee (2021, 2019)
- Reviewer for ACM Computing Surveys, IEEE Transactions on Cloud Computing (TCC), and Transactions on Dependable and Secure Computing (TDSC)
Other service
- "The voice of institutional wisdom", IEEE EuroS&P, 2020-2026
Contact
Email: pellegrino@cispa.de
Administrative questions: office-pellegrino@cispa.de
Phone: +49 681 87083 2178
Office
CISPA D1 Building
CISPA Helmholtz Center for Information SecurityKaiserstraße 21
66386 St. Ingbert, Germany
Postal address
CISPA C0 Building (only for letters and parcels)
CISPA Helmholtz Center for Information SecurityStuhlsatzenhaus 5
66123 Saarbrücken, Germany